Public AI tools can help Australian small and medium businesses draft emails, summarise documents, answer customer questions and improve workflows. The risk is not AI itself. The risk is sending information to a service without knowing what is collected, where it is stored, who can access it, or whether it may be used to improve a model.
Australian businesses should treat every new AI tool as a data-handling decision, not just a productivity purchase.
Start with the information, not the tool
Before staff paste anything into a public AI service, classify the information. Customer names, contact details, health information, financial records, passwords, private contracts and detailed CRM notes need stronger controls than a generic marketing idea. Create a simple rule that tells staff what may be entered, what must be removed, and what requires approval.
Ask five supplier questions
- What information does the service collect?
- Where is it stored and who can access it?
- Will the supplier use business data to train or improve models?
- How can the business delete information or close the account?
- What security, incident response and access controls does the supplier provide?
Keep the answers with your vendor records. A free trial can still create a privacy and security obligation if staff use it with real customer information.
Use a redaction step
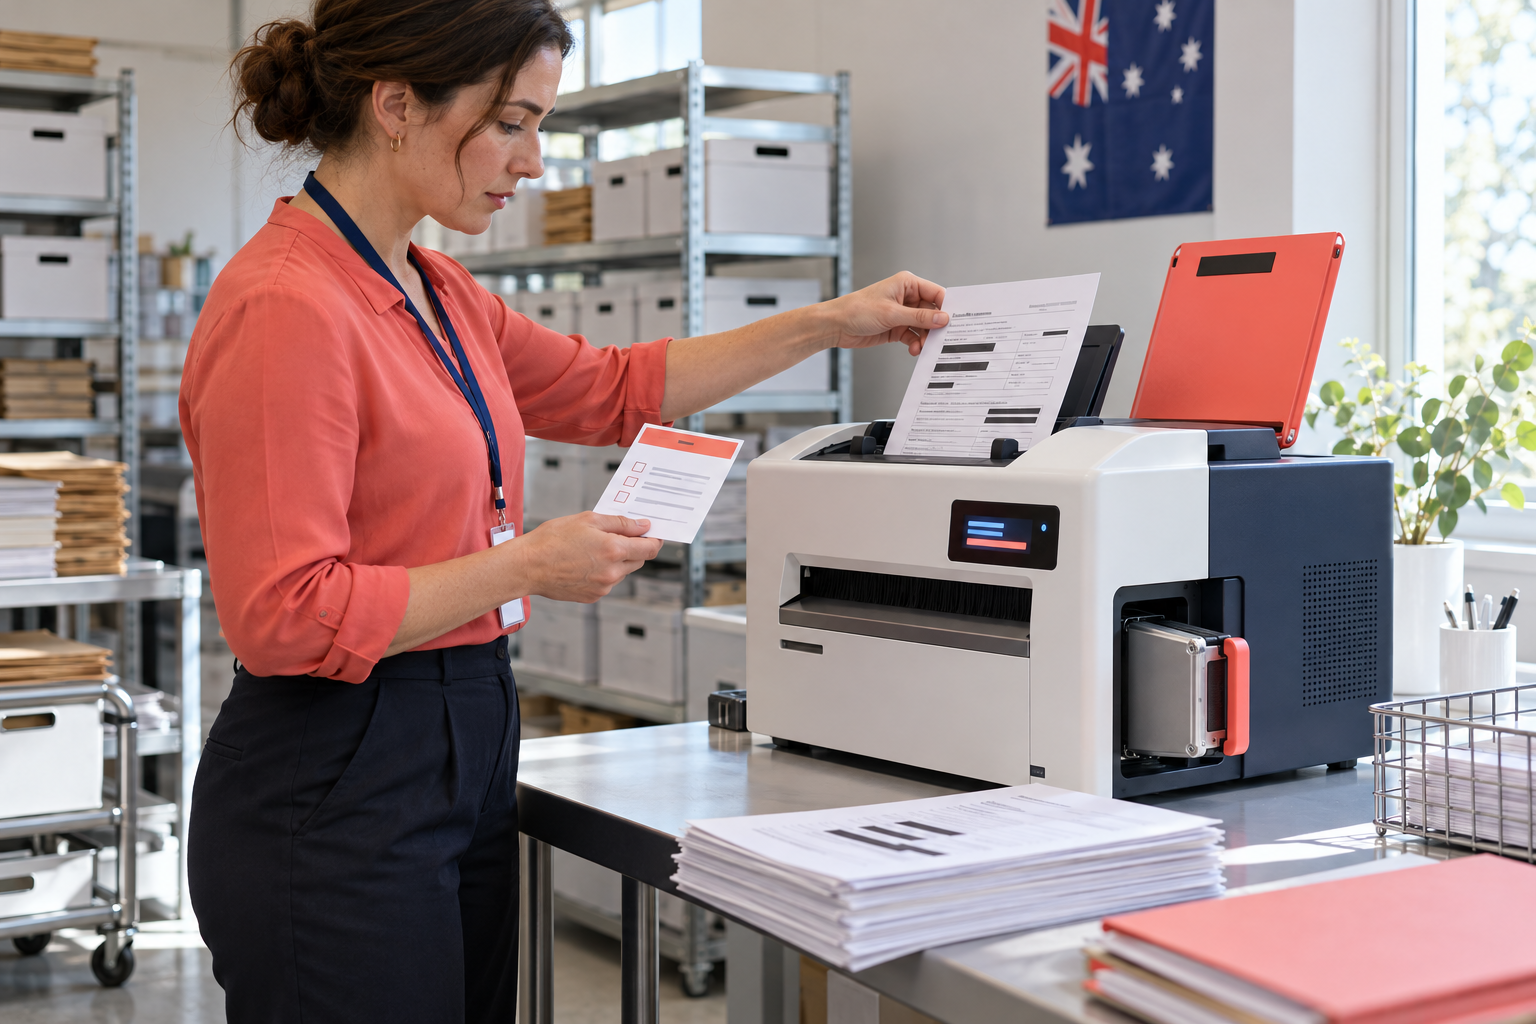
For many tasks, staff can remove names, account numbers, addresses and other identifying details before asking an AI tool for help. A controlled workflow can use a local redaction or document-processing step first, then send only the minimum information needed for the task. This is especially useful for customer service, recruitment, finance and health-related work.
Keep a human approval point
AI output should be checked before it is sent to a customer, added to a CRM, used in a financial decision or published on a website. Ask a named person to verify accuracy, privacy and tone. Keep a basic record of important AI-assisted decisions so the business can explain what happened later.
Make the process practical
- List the AI tools already in use.
- Map the information each tool receives.
- Remove unnecessary personal information.
- Approve a small set of business tools and accounts.
- Turn on multi-factor authentication and role-based access.
- Review supplier terms, retention and deletion settings.
- Train staff with examples from their real work.
Guidance from the Office of the Australian Information Commissioner and Business.gov.au gives businesses a useful starting point. The goal is not to block useful technology. It is to make AI adoption deliberate, proportionate and safe for customers and staff.
Sources
Leave a comment