Today’s cybersecurity news starts with an Australian account of AI voice impersonation. A Singapore youth portal breach, two cloud provider disclosures and a suspected FBI database intrusion show why a credible message, a working service or a quick database response cannot tell you whether the underlying data is safe. The five developments were reported or materially updated in the 24 hours to noon Sydney time. Report dates and incident dates are listed separately.
Cybersecurity news: what was reported and what is still unknown
1. Scott Pape reports a cloned voice in investment scam messages
Australia
Report: 22 November, 7:51 am AEDT (news.com.au reporting on Pape’s weekend column)
Incident: Not disclosed. Pape described a recent encounter reported to him by a friend.
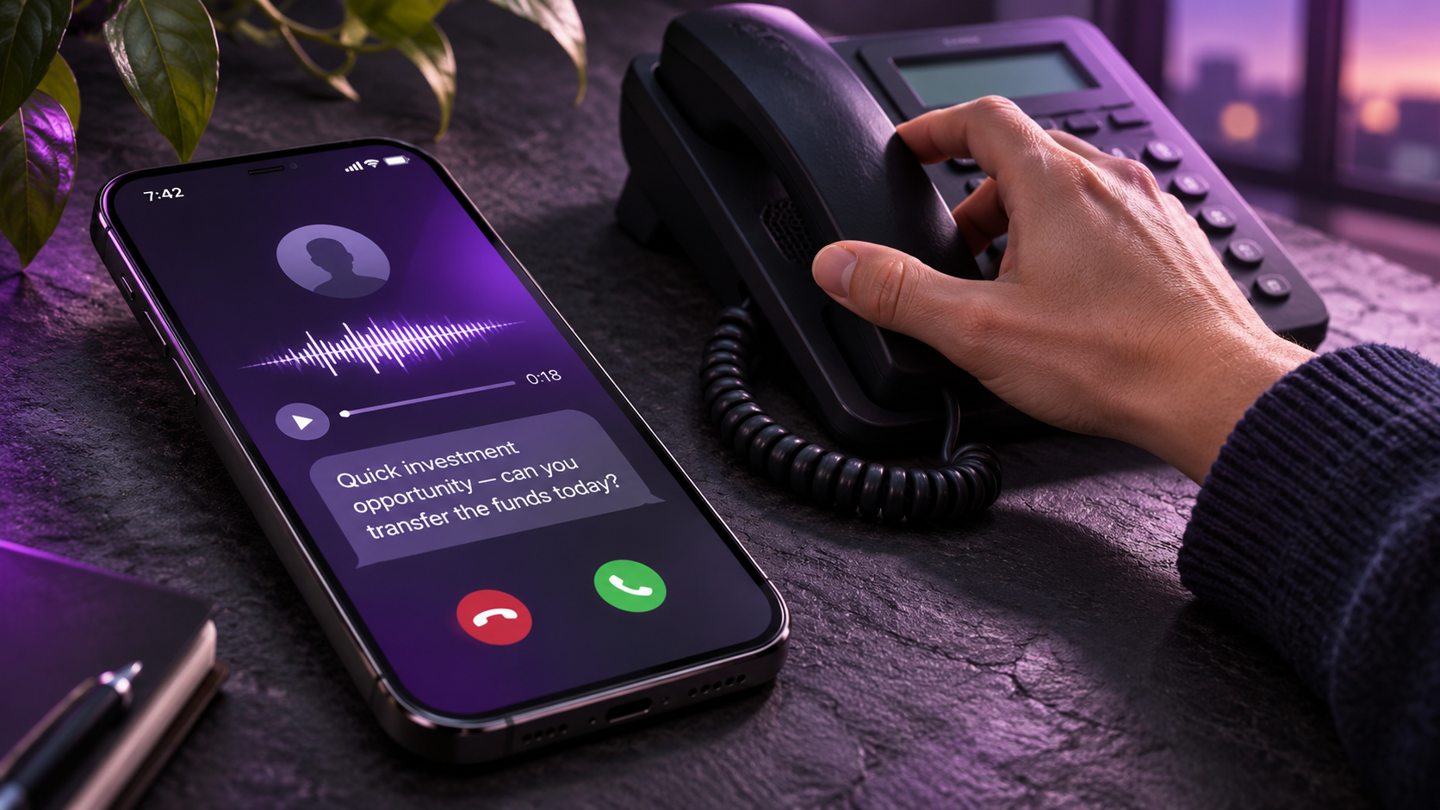
Australian personal finance writer Scott Pape says a friend thought he had been speaking with him on Facebook. In his weekend column, Pape said scammers were using an AI imitation of his voice to coax people into bogus investments. He has warned about manipulated videos before. The new account describes an apparent conversation with an impersonator, not the first sighting of a fake Pape profile. Neither report establishes how many people were approached or lost money in this instance.
For Australian finance teams, a voice message should never authorise a transfer or a change to bank details. The person approving the change should call a number already on file, not a number provided in the conversation, and require separate approval before releasing funds.
2. YMCA of Singapore contacts more than 13,000 after portal breach
Singapore
Report: 21 November, 9:32 am SGT (12:32 pm AEDT), YMCA notice; CNA at 7:34 pm SGT
Incident: YMCA was alerted on 19 October and took the system offline that day. Initial access date not disclosed.
YMCA of Singapore confirmed unauthorised access to its Youth For Causes registration portal. The associated database held participant and contact details, including some full or partial national identification numbers. Investigators could not establish or rule out whether personal data had been accessed, copied or taken. The organisation told CNA it was contacting more than 13,000 people as a precaution. That is not a confirmed count of stolen records.
Australian schools, charities and event organisers can ask their portal vendors how long application records are retained and whether they can trace access to individual records. A generic login history does not show what someone actually viewed or exported. Give families a known contact point to check unexpected messages after an incident.
3. Microsoft confirms Entra Connect Health metadata exposure
United States / global cloud service
Report: 21 November US date (BleepingComputer); Microsoft concluded its investigation on 20 November and confirmed the fix in a statement to the outlet
Incident: Microsoft detected the flaw on 9 November and fixed it on 19 November; exact dates of unauthorised access not disclosed.
Microsoft says a flaw in Entra Connect Health, a service that monitors identity infrastructure, allowed unauthorised read-only access to some organisations’ contact and configuration details. Those details included administrator email addresses and directory synchronisation information. Microsoft said it found no unauthorised configuration changes and that passwords, authentication tokens and valid keys were not exposed. The company fixed the flaw on its servers. It does not require a customer software update to close it.
An email can name your real administrators and describe your actual directory setup without being from Microsoft. If your team uses Connect Health, have the identity owner check Azure Service Health directly for notices and review privileged sign-ins. Don’t rely on a link supplied by an unsolicited message.
4. Rackspace restores Spot console after breach put customer credentials at risk
United States / global cloud service
Report: 21 November US date (BleepingComputer and reported service restoration)
Incident: 17 November, about 00:20 to 22:00 UTC; Rackspace learned of it on 18 November.
Rackspace told affected customers that someone used leaked credentials to access its Spot platform. In some customer environments that access allowed the intruder to start unauthorised workloads and read Kubernetes Secrets, which can hold database passwords and service keys. BleepingComputer reported that the administration console was restored on 21 November. The public reporting did not establish how many customers were affected or whether other customer data was taken.
For affected Australian teams, a working console is only one part of recovery. The platform owner should follow the provider notice, replace potentially exposed credentials, check that older credentials no longer work and review logs in connected systems. A secret used outside the cluster can still matter after the cluster is back online.
5. FBI investigating suspected intrusion into shared police database, reports say
United States
Report: 20 November, 9:12 pm EST (21 November, 1:12 pm AEDT), CNN; NBC and AP reported the inquiry separately
Incident: CNN says officials learned of it on 19 November US time. The initial intrusion date remains unclear.
CNN and NBC News report that the FBI is investigating a suspected intrusion into the National Crime Information Center, which US police agencies use to share information such as warrants and missing-person records. The FBI did not comment to NBC for its report. Public reporting has not established which records, if any, were viewed, changed or copied. There is no basis in these reports to connect the investigation to other recent outages.
For Australian organisations that share records across sites, the decision after an intrusion is not just when to restore access. The system owner needs a way to check whether critical records changed, using a protected history and comparison with the organisation that supplied the record. A system can return a result quickly and still return the wrong result.
How Xpansion can support your next step
Through Managed IT & Security, Xpansion Technologies can help you review system access, recovery plans and incident escalation within an agreed scope. Start with one high-risk workflow, such as changing supplier bank details or recovering access to a hosted customer system, and check who can approve or restore it.
Sources
- Scott Pape (The Barefoot Investor): Scott Pape’s account (subscriber access) | news.com.au report quoting the column
- YMCA of Singapore / Youth For Causes: YMCA of Singapore incident notice | CNA report and interview
- Microsoft: Microsoft statement and customer notice quoted by BleepingComputer | Neowin coverage
- Rackspace Technology / Rackspace Spot: Rackspace customer notice quoted by BleepingComputer | Atlabyte coverage based on BleepingComputer
- Federal Bureau of Investigation / National Crime Information Center: CNN original reporting | NBC News separately sourced reporting