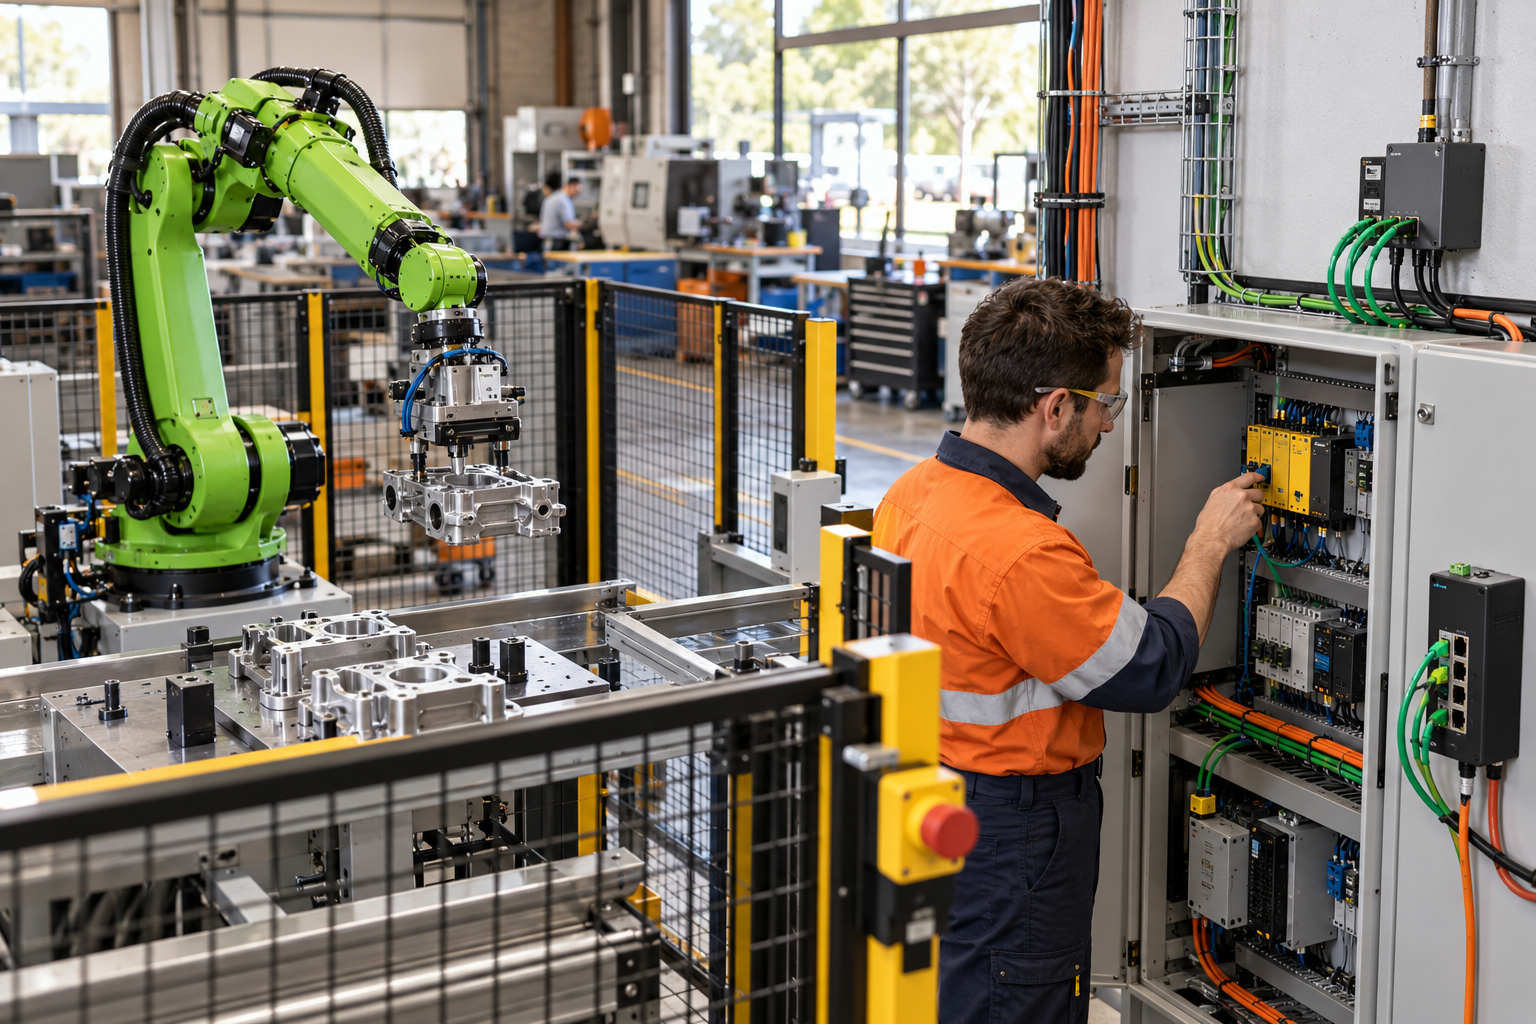
Operational technology is no longer limited to large factories. Australian small and medium businesses increasingly rely on connected machinery, sensors, building controls, production equipment and remote maintenance tools. That connectivity can improve visibility and productivity, but it also creates a pathway that needs practical security controls.
Why connected equipment needs a network plan
A machine, programmable logic controller, sensor or gateway may now exchange data with a cloud service, supplier portal or business network. If those connections are added without a clear design, an issue in one system can affect production, safety, customer commitments or the ability to recover after an incident.
Cyber.gov.au’s operational technology guidance highlights limiting exposure, standardising connections, using secure protocols, hardening boundaries, monitoring connectivity and having an isolation plan. SMEs do not need to copy a large enterprise architecture, but they do need to know what is connected and why.
Five practical checks for SMEs
- Map the equipment and pathways. Record each machine, controller, sensor, gateway, remote-access tool, supplier connection and cloud service. Identify who owns each connection.
- Separate operational and office systems. Avoid placing machinery controls on the same unrestricted network as staff laptops, guest Wi-Fi, email or point-of-sale systems. Ask a qualified provider to design the separation.
- Control remote access. Remove permanent shared access where possible. Use named accounts, MFA, time-limited approvals, logging and a clear process for supplier support.
- Monitor changes. Know when a new device, connection or configuration change appears. Keep a simple record of approved changes so unusual activity can be investigated quickly.
- Practise isolation and recovery. Decide which connection can be disconnected safely, who makes that decision, and how the business continues if remote monitoring or cloud access is unavailable.
Questions to ask technology suppliers
Ask how devices are updated, how vulnerabilities are reported, how long logs are retained, how accounts are recovered, what happens when a contract ends, and whether the business can export important configuration and operational data. Confirm who is responsible for the equipment, network, cloud service and incident response.
Keep the first step manageable
Start with one production line, site, building system or connected machine. Draw its data and remote-access pathways, remove unnecessary exposure, test the alert and recovery process, and document the result. Once the pattern works, apply it to the next system.
Business.gov.au reminds SMEs that cyber security protects technology, data and information from unauthorised access, corruption, theft and damage. Connected equipment belongs in that same conversation, even when it sits on a workshop floor rather than in an office.
Sources
- Cyber.gov.au: Secure connectivity principles for Operational Technology (OT)
- Cyber.gov.au: An introduction to securing smart places
- business.gov.au: Cyber security and your business
Leave a comment