The office computers have been replaced. Someone deletes the old customer folders, empties the recycle bin and arranges collection. Secure device disposal is not complete just because the files have disappeared from the screen. The important question is whether someone receiving the storage could recover information your business was responsible for protecting.
Consider a hypothetical accounting practice selling an old computer. A recoverable export could expose customer identity documents or bank details. This is a data-protection decision, not simply an equipment resale decision. It needs an accountable owner before the device leaves your control.
Why deletion is not the same as sanitisation
Ordinary deletion can remove the file’s reference without reliably removing its underlying contents. A quick format or operating-system reinstall should not be accepted as evidence of sanitisation without checking what that particular process actually does.
Solid-state drives add another complication. Their controllers move writes between memory cells to manage wear and can retain spare or retired storage areas outside the operating system’s normal view. Repeatedly overwriting the visible drive is therefore not proof that every previous copy has gone. NIST’s 2025 media-sanitisation guidance specifically warns against carrying old overwrite assumptions across to flash storage.
The failure chain is straightforward: sensitive information remains on storage, the business releases that storage, and another party gains physical access. Whether recovery succeeds depends on the device, its encryption history, the disposal method and the recipient’s capabilities. Exposure is a conditional risk, not an inevitable outcome.
Choose the secure device disposal outcome first
Ask whether the storage will be reused inside the business, sold externally or destroyed. Then have a competent technician choose a documented method suited to the actual model and data sensitivity. NIST distinguishes three outcomes:
- Clear: protects against straightforward recovery through normal interfaces. It is not automatically the right assurance level for external release.
- Purge: aims to make recovery infeasible even with advanced laboratory techniques while potentially retaining a usable drive. Supported device sanitisation commands or properly implemented cryptographic erase may qualify.
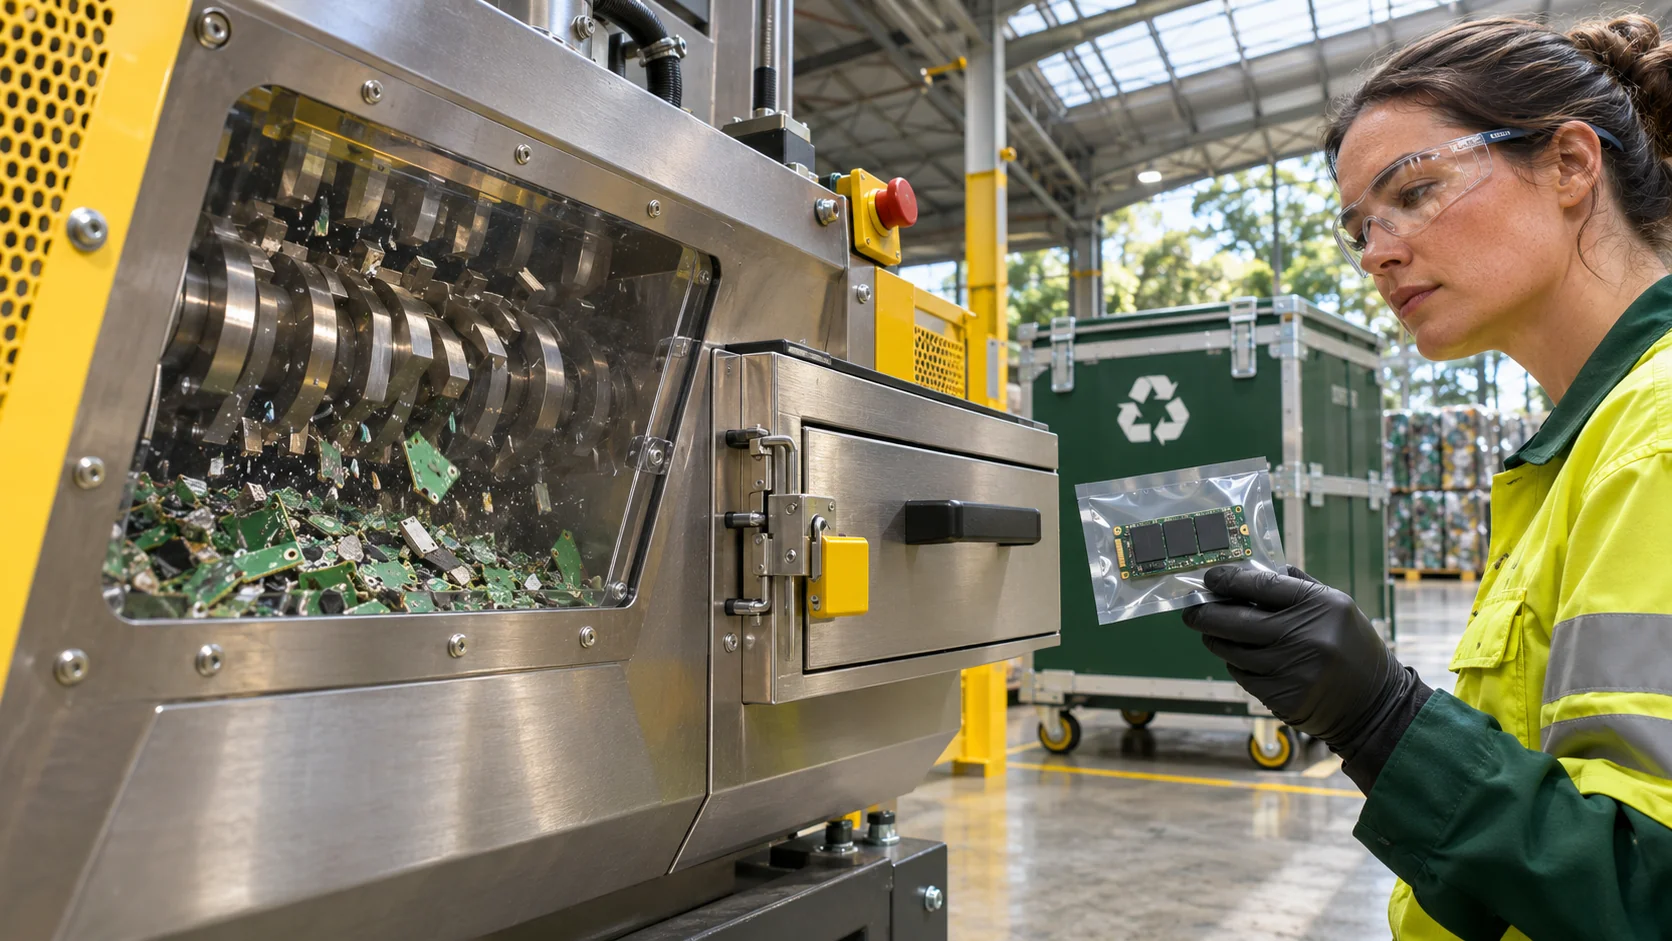
- Destroy: makes the storage unusable and recovery infeasible. This may be necessary when the drive is faulty or a suitable sanitisation outcome cannot be established.
These are assurance categories, not interchangeable buttons. Confirm vendor implementation and completion results. Cryptographic erase depends on suitable encryption and key handling, including whether relevant data was encrypted and whether usable key copies remain. Merely changing a login password is not cryptographic erase.
A collection receipt is not proof of removal
Before release, separate operational completion from the decision that the result is acceptable. NIST calls these verification and validation. A tool saying it finished is useful evidence, but someone must still assess errors, exclusions and whether the chosen method met the required protection.
- Business owner: confirms retention obligations, required backups and permission to retire the asset. Do not destroy records subject to a legal hold.
- IT owner: records device and drive identifiers, method, tool/version, completion status and any unresolved exceptions.
- Disposal provider: maintains traceable custody and supplies evidence tied to the actual media, not just the number of boxes collected.
If destruction is chosen, require a process appropriate to the storage and information. A drilled hole or visibly damaged casing can leave memory chips recoverable. Even shredding requires a suitable specification; a generic recycling claim is not a guarantee. Until the result is accepted, keep the media secured rather than placing it in an open collection area.
The Australian privacy decision still belongs to you
For businesses covered by the Australian Privacy Principles, APP 11 requires reasonable security measures and, when personal information is no longer needed for a permitted purpose, reasonable steps to destroy or de-identify it, subject to Commonwealth-record and legal-retention exceptions. Do not assume every SME has identical Privacy Act coverage.
ASD’s Information Security Manual provides detailed media guidance; it is not a blanket legal mandate for every Australian business. Use applicable contractual, privacy and security requirements to set your assurance level, rather than treating a US standard as Australian law.
Include asset retirement in your managed IT and security requirements, with one named release owner. The useful final record is not “computer collected”. It is which storage left, what happened to its data, who accepted the evidence and where it went.