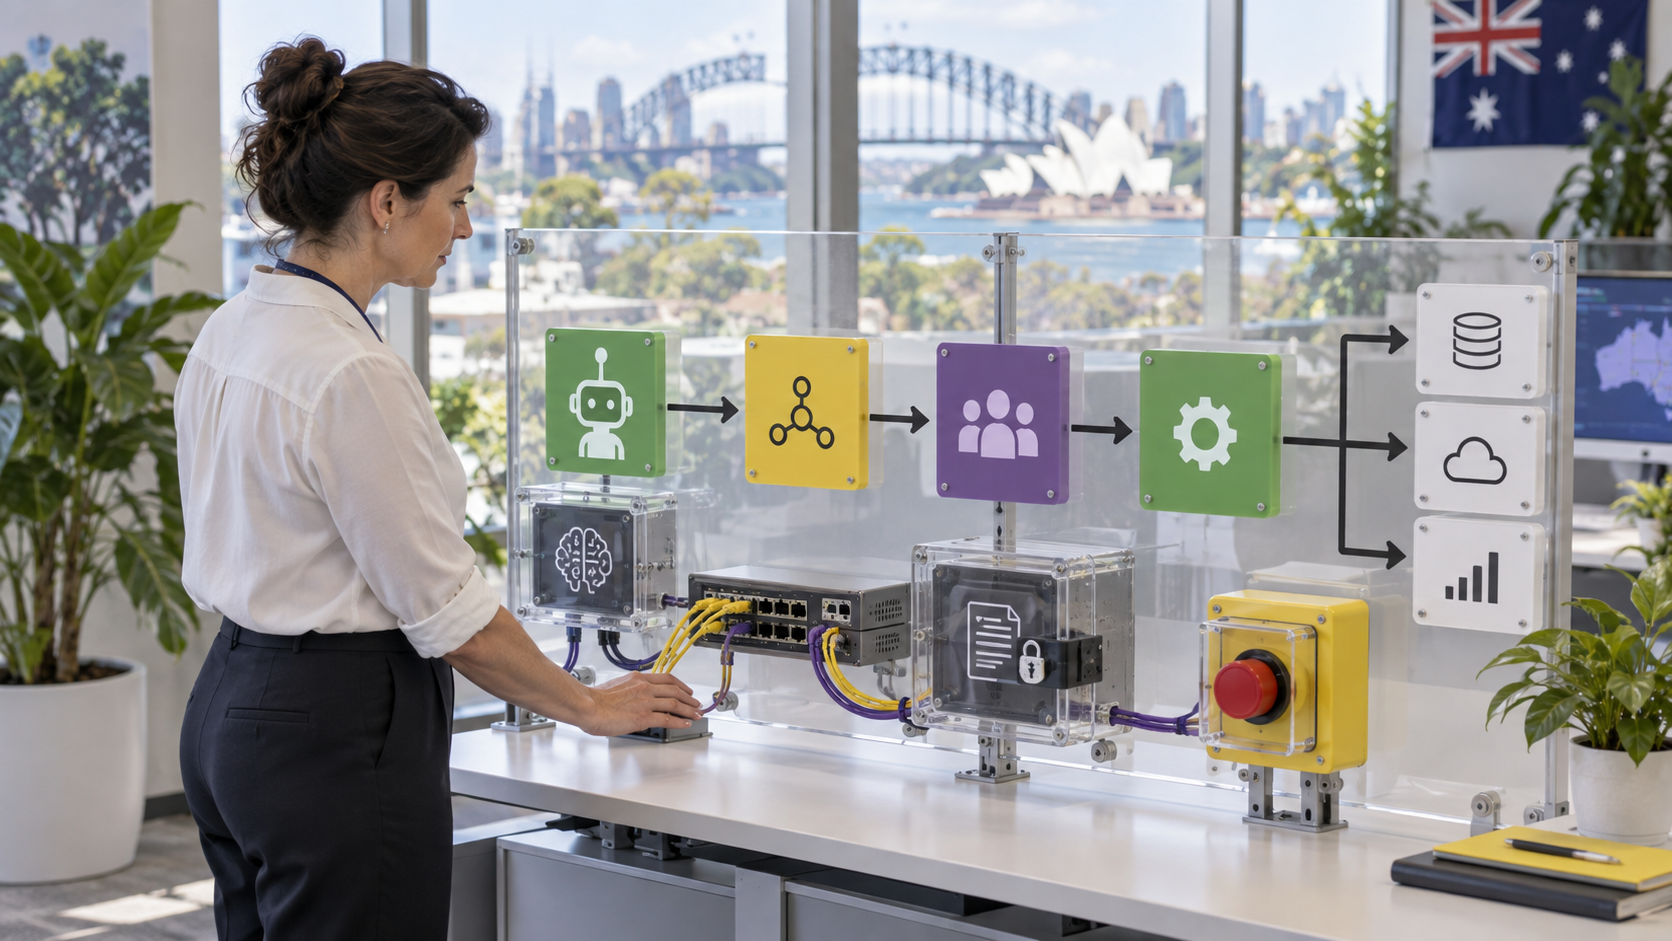
Agentic AI is different from a chatbot that only drafts a response. When connected to business data, APIs and workflow tools, an agent can plan a task, call systems and take actions. That can save time for a small business, but it also makes permissions, oversight and recovery much more important.
Recent guidance from the Australian Signals Directorate’s Australian Cyber Security Centre highlights the software layer around the model, often called the harness. It supplies data and tools, controls execution and records activity. For an SME, this is the part of the system that must be designed and governed before the agent is allowed to do useful work.
Start with a narrow job
Choose one measurable use case, such as classifying enquiries, preparing a draft work order or identifying incomplete CRM records. Write down what the agent may read, what it may change and what it must never do. A narrow boundary makes testing and accountability practical.
Apply least privilege
Use a dedicated identity for the agent and give it only the permissions required for the approved task. Separate development, testing and production access. Do not connect a general-purpose agent to every customer record, finance workflow and administrator function simply because the integration makes it possible.
Keep people in the approval loop
Require a human confirmation before payments, refunds, contract commitments, account changes, sensitive communications or destructive actions. Approval should show the proposed action, the data used and the person responsible. It should not be a rubber stamp hidden inside an automated workflow.
Log actions and test manipulation
Record prompts, tool calls, decisions, approvals and outcomes in a form staff can review. Test prompt injection, misleading documents, unexpected permissions, duplicate actions and service outages. Check whether the agent can be stopped quickly and whether a manual process is ready when it fails.
Practical pre-launch checklist
- Define one approved business outcome and clear prohibited actions.
- Map every data source, API and permission the agent can reach.
- Use separate identities and environments with least privilege.
- Require approval for high-impact or irreversible actions.
- Log activity, review exceptions and test prompt injection.
- Document a shutdown, rollback and human fallback procedure.
Agentic AI can be valuable for Australian SMEs when it is treated as an operational system, not an unmonitored assistant. Start small, measure the outcome and expand only when the controls are working in practice.
Sources
Leave a comment