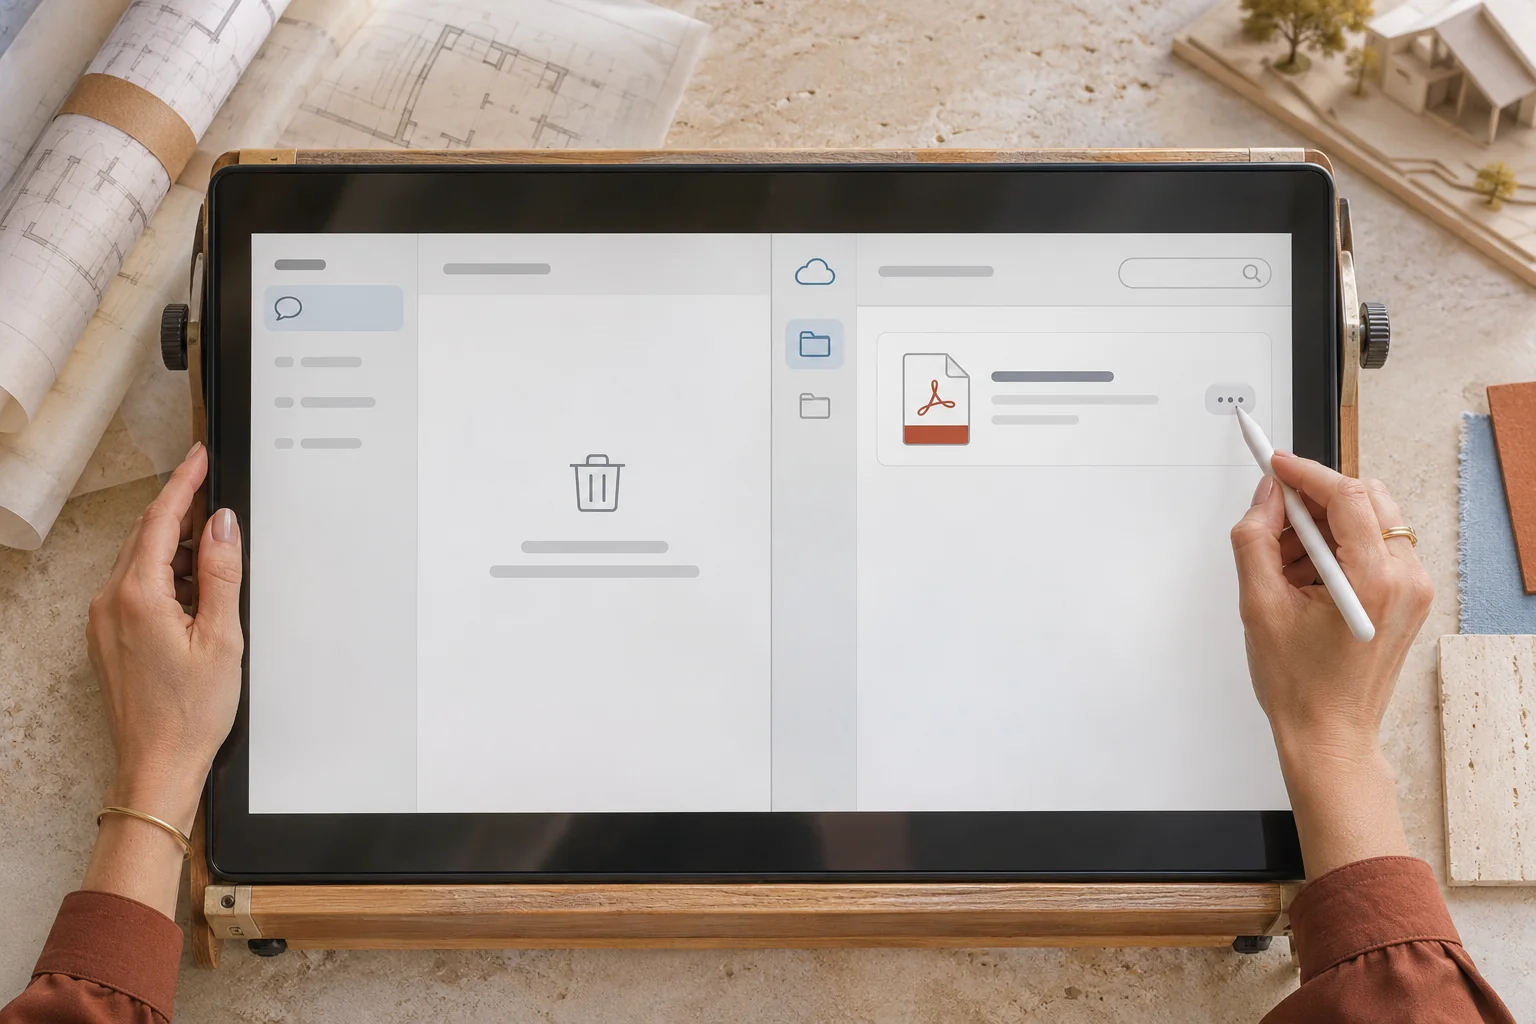
An architect uploads a customer’s residential brief to an AI assistant to draft a project summary. When the job is finished, she deletes the conversation. The sidebar is clear, so she tells the customer the uploaded file has been removed.
That is a hypothetical example, but the distinction is real: AI file retention can operate separately from chat history. A conversation, a saved upload and a shared project may have different deletion controls. Clearing one screen is not evidence that every copy is gone.
For Australian business owners, the risk is an inaccurate privacy promise followed by continued access to customer addresses, budgets or other confidential details. It does not mean deleted files automatically become public. It means the business needs to know which stored object it actually removed.
Why AI file retention survives a cleared conversation
An AI service can store the conversation and its source documents as separate objects. The chat references a file; it does not necessarily own the only copy. Removing that reference can leave a reusable file in another part of the account.
OpenAI’s current ChatGPT guidance provides a concrete example. Files saved separately in Library or Space are not deleted when the associated chat is deleted. They need their own removal action. Project files and custom GPT knowledge also have separate retention rules. Availability and controls depend on the account and workspace, so this example should not be assumed to describe every AI product.
The commercial failure chain is straightforward: a staff member uploads customer material, deletes the visible conversation, assumes the upload disappeared, and leaves a saved copy available under the remaining account or sharing permissions. A later account compromise or an overly broad project audience could then expose information the business believed it had removed.
Removal from view is not immediate erasure
OpenAI says deleted chats disappear from the account view immediately and are scheduled for permanent deletion within 30 days, subject to its stated de-identification, security and legal exceptions. Its guidance separately describes deletion timing for project files and custom GPT data, and backup retention in enterprise compliance scenarios.
Those are product-specific statements, not a universal deadline or a promise of instant erasure. Nor does choosing not to use content for model training establish that no operational copy is retained. Treat training use, active access and eventual deletion as separate questions to verify in the applicable terms.
This matters when answering a customer request. Saying “we removed the chat” is narrower and more defensible than saying “all your data has been permanently erased” without evidence.
Give deletion an owner and a test
- Map the actual destinations. The application owner should identify chat history, saved-file libraries, projects and any exported summaries. Record which account, workspace and sharing controls apply. Include connected systems only where the workflow actually uses them.
- Separate business records from convenience copies. The records or privacy owner should decide what must be retained and what can be removed. Do not destroy a legally required source record simply to clean up an AI workspace.
- Test with harmless material. IT should upload a synthetic document, remove its chat and check whether the file remains accessible in the relevant library or project. Then test the separate deletion action and record the result. Never use a live customer file for this exercise.
- Document the limit of the evidence. A user-interface check can demonstrate loss of active access. It cannot independently prove that a provider has erased backups. Retain the applicable policy, administrator evidence and any provider confirmation, with its exceptions.
Check the Australian privacy obligation
For organisations covered by the Privacy Act, APP 11 requires reasonable steps to destroy or de-identify personal information no longer needed for a permitted purpose, subject to the stated Commonwealth-record and legal-retention exceptions. Coverage must be checked; not every small business has identical obligations.
The OAIC also recommends against entering personal information, particularly sensitive information, into publicly available generative AI tools as a matter of best practice. Deleting later does not replace deciding whether uploading was appropriate.
Include retention and deletion evidence in your AI adoption planning. The useful acceptance test is not an empty sidebar. It is a documented account of what was removed, what remains, who can access it and when the remaining retention period ends.
References
- OpenAI: Chat and file retention in ChatGPT. Product-specific guidance checked 17 November 2026.
- OAIC: Guidance on privacy and the use of commercially available AI products.
- OAIC: APP 11, Security of personal information.