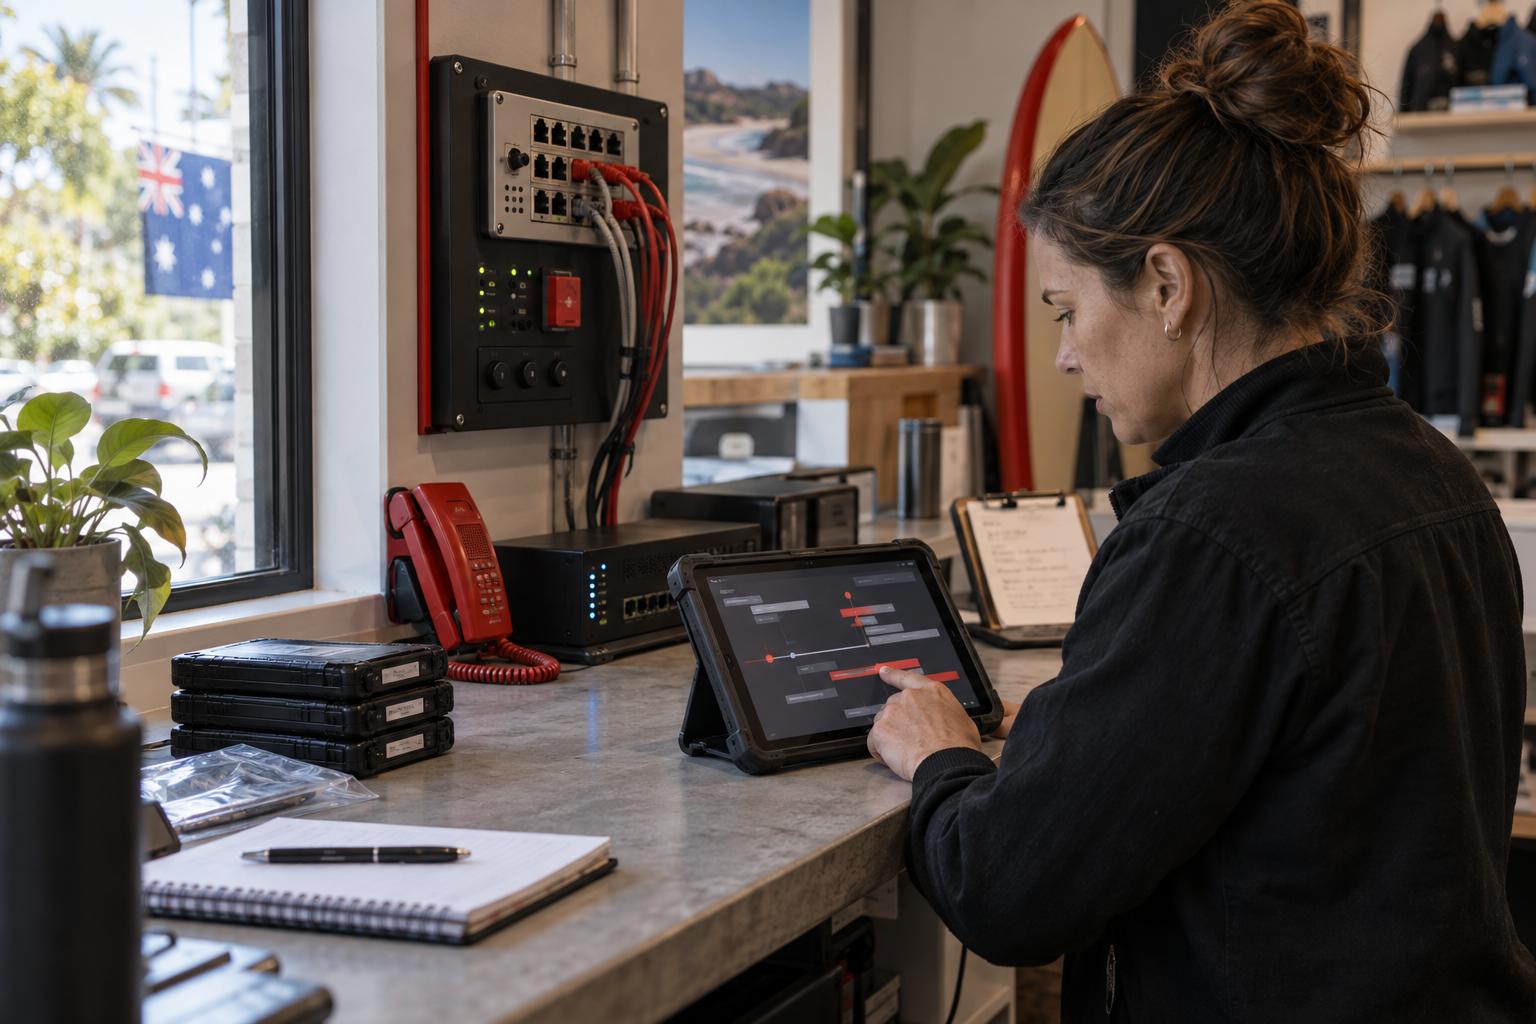
Cyber incident response must treat an incident as a business event, not only a technical problem. A compromised account, ransomware alert, suspicious payment or exposed customer record can interrupt operations and create difficult decisions about evidence, communications and recovery.
Cyber incident response: prepare before the alert
Assign an incident owner and a backup contact. Keep current contact details for your IT provider, cloud vendors, insurer, bank and relevant reporting channels. Write a short first-response checklist that staff can follow without guessing.
Detect and contain carefully
Record what was noticed, when it happened, which account or device was involved and who first reported it. Contain the affected account or device using an agreed process, but avoid wiping systems, deleting messages or changing logs before evidence is preserved.
Protect evidence and decisions
- Keep relevant alerts, email headers, access logs and screenshots.
- Record actions, times, decision owners and vendor advice.
- Separate confirmed facts from assumptions.
- Use a secure incident record with restricted access.
- Check that backups are protected and available before recovery.
Communicate with control
Tell staff what they need to know and where to send questions. Do not improvise customer, supplier or public statements while facts are still being checked. Consider privacy and reporting obligations with the right adviser, especially where personal information may be involved.
Recover and learn
Restore systems in a controlled order, reset exposed credentials, review third-party access and monitor for repeat activity. After the incident, document the cause, the delay points and the improvements needed in systems, training and supplier arrangements.
Questions to ask this week
Who owns the first response? Can staff report a suspected incident quickly? Are logs and backups protected? Which systems would stop the business if unavailable? Do your suppliers provide an incident contact and clear notification process?
Leave a comment